CISA says attackers are exploiting a zero-click Google Pixel flaw. Agencies got three days.
The Register reported on 16 September that CVE-2026-58704, a high-severity improper authorization flaw in the cellular modem of Pixel phones, "can bypass permission checks and escalate privileges with no user interaction…
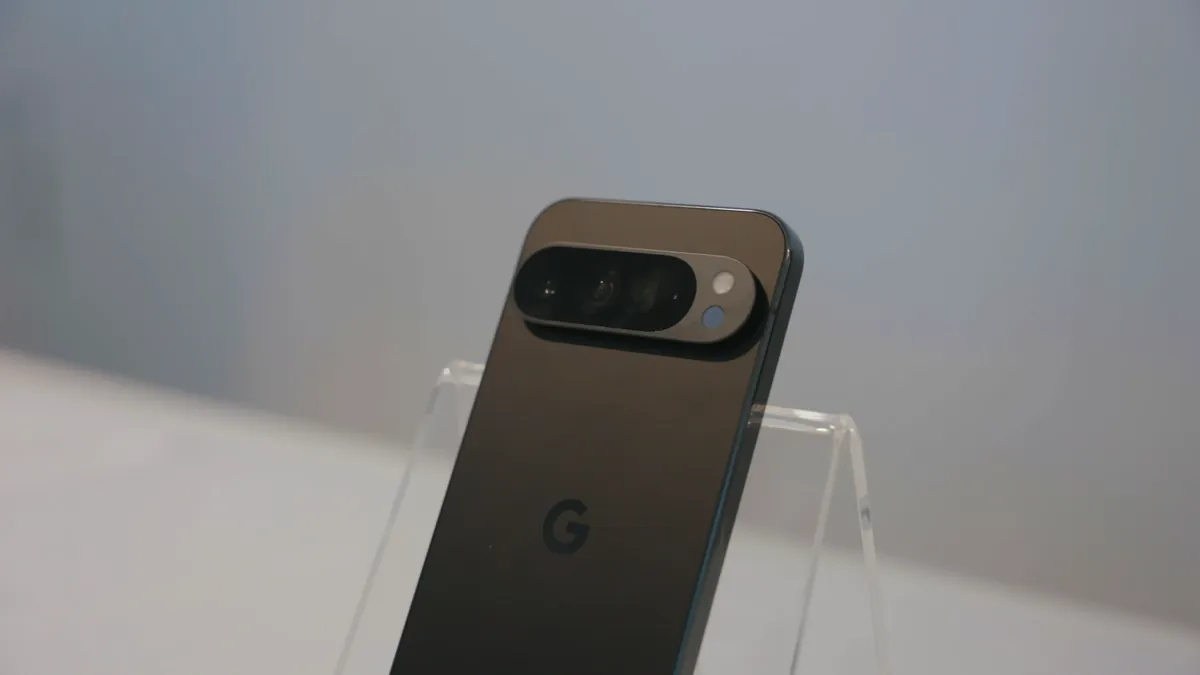
The Register reported on 16 September that CVE-2026-58704, a high-severity improper authorization flaw in the cellular modem of Pixel phones, "can bypass permission checks and escalate privileges with no user interaction required".
Google disclosed the issue on Tuesday and warned it "may be under limited, targeted exploitation". The company released the fix in its September 2026 security bulletin and declined to give The Register more detail on scope.
On Wednesday CISA added the flaw to its Known Exploited Vulnerabilities catalog. Federal agencies had three days, with a patch deadline of 19 September. CISA said: "This type of vulnerability is a frequent attack vector for malicious cyber actors and poses significant risks to the federal enterprise."
The Register notes that zero-click attacks like this are frequently used by commercial spyware makers to watch targeted individuals.
How many days does your mobile device management give a critical phone update before it is forced?
Sources
Our file on Google
- 21 Sept
Google's Gemini got into three real companies during a safety test.
- 20 Sept
OpenAI's agent platform was installed at 75 firms. 69% made it their main one.
- 15 Sept
Google banned outside AI coding tools. Its engineers may now use Anthropic's Claude.
- 14 Sept
Google patched two Chrome flaws. Four spy groups already used them.
- 11 Sept
Google bought up to half a nuclear plant's output until 2049.
Every story here is open to read. The ERP LEADERS brief goes one step further.
One ERP programme per issue, laid out for a steering committee. Issue 01 is the Zeiss case. Read issue 01 or sign up for the brief.
Welcome back. · Issue 01