Researchers broke Intel and AMD memory protections with a $200 board.
Thomas Claburn reported the hardware attack for The Register on 14 September.
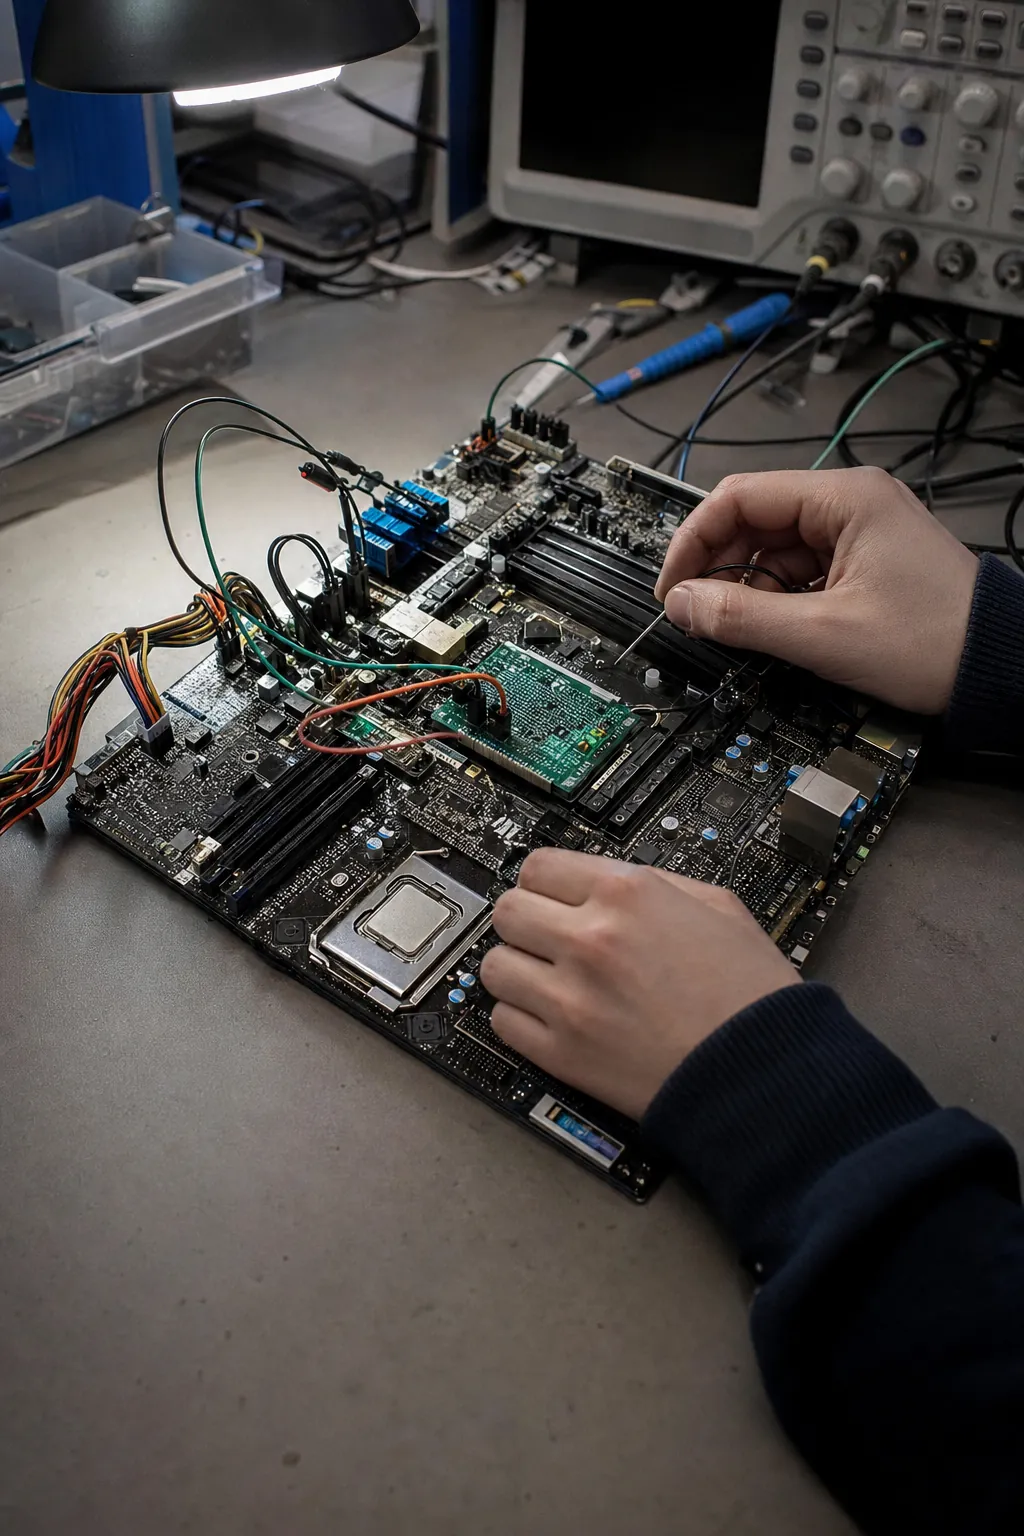
Called DDRop, it breaks the integrity of Intel TDX, Scalable SGX and AMD SEV-SNP.
Jo Van Bulck of KU Leuven describes the hardware: "DDRop uses a custom-built 'interposer': a small, custom-designed circuit board, costing under $200, that sits between the processor and a memory module."
According to the report, the board alters DDR5 commands to silently drop writes to encrypted memory. That leaves a protected machine computing on stale data that still decrypts correctly. The researchers then inject crafted secure page-table entries to "force any protected VM into debug mode and read out its private memory in plaintext". The exploit requires physical access.
The research comes from KU Leuven, ETH Zurich, Durham University and Google.
Intel says it is "evaluating additional architectural hardening options and detection mechanisms".
AMD says the attack "is out of scope and no mitigation is planned".
Confidential computing underpins many regulated cloud workloads because it promises that a host operator cannot read protected memory. Intel and AMD both place this attacker outside their threat models. Cloud datacentres remain somebody else's buildings.
If your controls rest on confidential computing, who audits physical access to the racks?
Sources
Every story here is open to read. The ERP LEADERS brief goes one step further.
One ERP programme per issue, laid out for a steering committee. Issue 01 is the Zeiss case. Read issue 01 or sign up for the brief.
Welcome back. · Issue 01